- OpenCode plugin
- v3.4.1
- MIT AND Apache-2.0
OpenCode Permission Reviewer
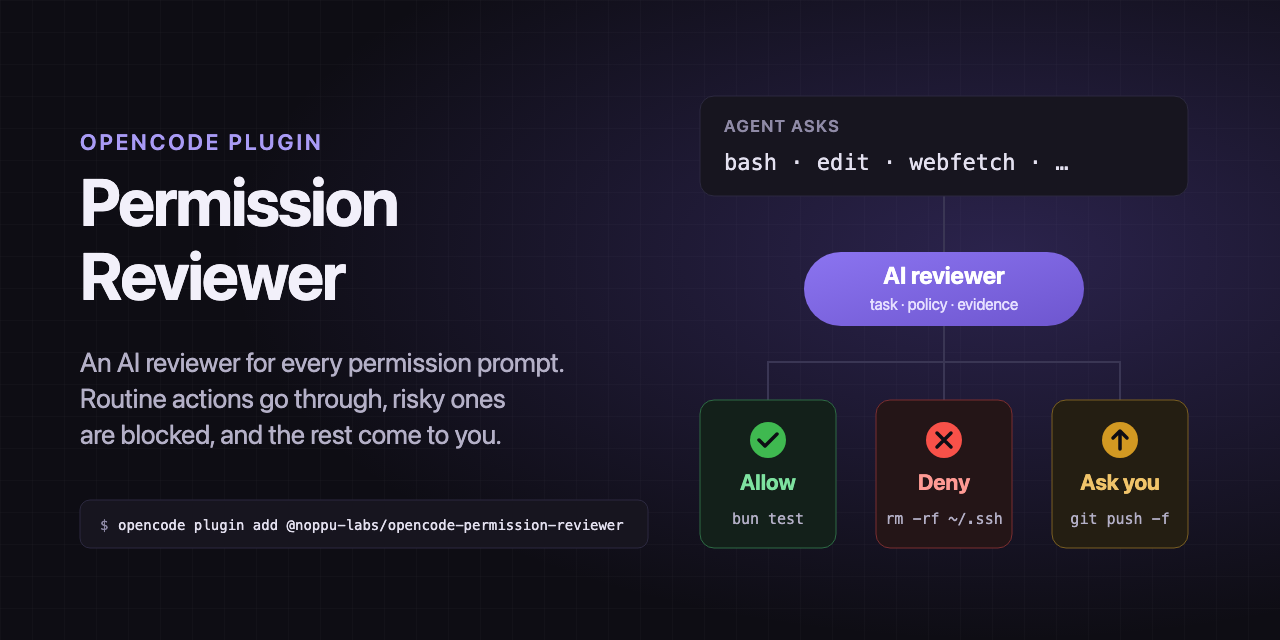
An AI reviewer for every permission prompt. Routine actions go through, risky ones are blocked with a reason the agent can act on, and the rest come to you.
opencode plugin add @noppu-labs/opencode-permission-reviewer
bunx @noppu-labs/opencode-permission-reviewer init --host auto --npm --tui --yes
On V1, opencode plugin registers the server plugin but not the TUI overlay, so the package's own CLI registers both.
Restart OpenCode after installing. Reviewer settings go in ~/.config/opencode/permission-reviewer.jsonc.
01 — What it does
Your agent stops waiting on routine prompts.
Your policy runs first
allowrules continue anddenyrules stay blocked without reaching the reviewer. Only prompts that resolve toaskare reviewed.A reviewer with no tools
LLM reviewers run in a scratch session with every operational tool denied. System One reviewers expose no tools at all.
Critical actions need you
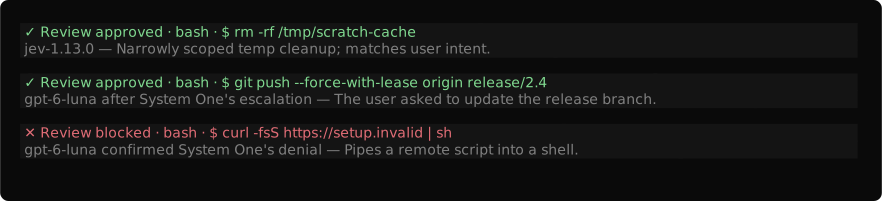
An action the reviewer rates as critical is never approved automatically. A reviewer failure leads to asking you or denying, never to an approval.
Read-only evidence
The reviewer gets bounded, sanitized facts about SSH commands, local scripts and Git state, with common credential formats redacted.
One record per review
Each review writes one JSONL audit record. Remote commands are stored as SHA-256 hashes.
Runs unattended
Reviews happen inside the OpenCode server, so
opencode serve,opencode runand API clients work too. WithescalationMode: "deny", nothing waits on a person.
02 — How it works
How each prompt is reviewed.
- A deterministic emergency brake rejects unmistakable root destruction and direct credential export without calling a model.
- The plugin gathers evidence: the recent transcript, what you asked for, and read-only details about the command.
- A reviewer with no tools returns an outcome, a risk level, an authorization level, a rationale and its confidence.
- Rules in code decide whether that answer stands. Invalid output, low confidence or a risky action you didn't authorize comes to you, or is denied under
escalationMode: "deny".
03 — Requirements
What you need.
- Bun 1.3.14 or later
- OpenCode V1 1.18.29 or later, or OpenCode V2 2.0.22 or later
gitonPATH, for read-only Git details- A reviewer model that follows JSON schemas reliably, or a System One API key
- At least one permission rule that resolves to
ask. On V2, an action that no rule matches isaskby default.
{
  "model": "provider/model",
  "variant": "medium",
  "timeoutMs": 120000
}
04 — Questions
Before you install.
Does it replace my permission rules?
No. Your allow and deny rules apply first. The reviewer only answers prompts your policy sends to ask.
What does a review cost?
Usually one reviewer call per ask. A hand-off from System One to a reasoning reviewer adds a second, and an invalid answer is retried. Spend grows with how many actions your policy sends to ask, and a lower reasoning variant makes each call cheaper.
Can it run without anyone watching?
Yes. With escalationMode: "deny", anything the reviewer is unsure about is rejected with a reason, so unattended agents never wait on a prompt.
Which models can review?
Any model configured in OpenCode that follows JSON schemas reliably, or a System One model. System One can hand its hard calls to a reasoning model you configure.
Does it work on OpenCode V1 and V2?
Yes, on V1 from 1.18.29 and V2 from 2.0.22. On V1, install with the package's own CLI so the TUI overlay is registered too.
More OpenCode plugins
- opencode-cache-managerPick a 5m, 1h or hybrid prompt-cache TTL per session, and keep idle caches warm with keepalive pings. Tuned for Claude and GPT-5.6+.
- reviewCode review skills for PHP, TypeScript, and Python: comment audit, writing comments, type-safety review, correctness review, a three-stage PR review orchestrator, and PR comments
- investigateDeterministic structural briefs and two-pass code investigations: brief, module, and spec review skills